Search GrowthX Learning Content
KYC, Data Privacy and Consent Requirements for Fintechs
The rapid growth of fintech has completely changed the way financial services are delivered in India. Customers can now open accounts, apply for loans, make payments, invest, purchase insurance, verify their identity and access financial products through mobile applications without visiting a physical branch. This convenience, however, depends heavily on the collection and processing of personal and financial information. A fintech platform may collect a customer's name, mobile number, PAN, Aadhaar-related information, photograph, address, bank account details, income records, transaction history, credit information and other data during a single digital onboarding journey. When this information is combined with technologies such as automated underwriting, artificial intelligence, APIs, Video KYC and digital lending platforms, questions relating to customer identification, privacy and consent become extremely important.
For this reason, Know Your Customer (KYC), data privacy and consent requirements should not be treated as separate compliance exercises. They form different parts of the same customer-data lifecycle. KYC determines who the customer is and helps financial institutions prevent misuse of the financial system. Data privacy regulates how customer information is collected, used, stored and shared. Consent determines whether customers have been properly informed and whether their permission has been obtained wherever permission is legally required. For fintech companies, compliance becomes even more complex because not every fintech is itself directly regulated in the same manner. A bank, NBFC, payment service provider, Account Aggregator, Lending Service Provider, digital lending application and technology vendor can have different responsibilities. Therefore, the first step for any fintech should be to understand its exact role in the financial ecosystem and identify which regulatory requirements apply to its activities.
In this article, CA Manish Mishra talks about KYC, Data Privacy and Consent Requirements for Fintechs
Why KYC Is Important for Fintech Companies
Know Your Customer, commonly known as KYC, is one of the basic controls used by financial institutions to verify the identity of customers. Its purpose is not limited to obtaining identification documents. KYC is part of the wider framework for preventing money laundering, terrorist financing, impersonation, fraudulent transactions and misuse of the financial system. India's KYC framework is closely connected with the Prevention of Money Laundering Act, 2002, the Prevention of Money-Laundering (Maintenance of Records) Rules and RBI's Master Direction on KYC. RBI's framework requires regulated entities to establish appropriate customer acceptance, customer identification, risk-management and transaction-monitoring systems.
For fintech businesses, an important point is that the term “fintech” does not automatically create one uniform regulatory category. For example, a Lending Service Provider may provide the technology through which a borrower applies for a loan, while the actual loan is granted by an RBI-regulated bank or NBFC. The regulated lender continues to remain responsible for compliance even though substantial parts of the customer's digital journey may be handled by the fintech. Therefore, fintech agreements, technology systems and internal controls should clearly establish which organisation is responsible for collecting customer information, verifying it, maintaining records, carrying out ongoing monitoring and responding to regulatory requirements.
Customer Identification and Customer Due Diligence
Customer identification is the starting point of KYC, but Customer Due Diligence, or CDD, goes further. CDD is intended to help a regulated institution understand who the customer really is and whether the relationship presents any unusual or elevated financial-crime risk. For an individual customer, due diligence may involve verifying identity, address, PAN and other prescribed details through legally recognised mechanisms. The specific documents or methods required depend on the type of financial institution and the product being provided.
A fintech platform should therefore avoid designing an onboarding process around the assumption that collecting one document automatically completes KYC. Verification must be carried out in accordance with the requirements applicable to the regulated financial institution. The customer's information must also be sufficiently reliable and consistent. If the PAN details, address records, photograph and banking information contain significant inconsistencies, the onboarding process should have mechanisms for raising alerts and obtaining clarification before the financial relationship is activated. Proper CDD protects both the customer and the financial institution. Weak verification can allow fraudsters to use stolen identities, synthetic identities or forged documents to obtain loans, open financial accounts or move illegal funds.
Aadhaar and Digital KYC
Aadhaar is widely used within India's digital ecosystem, but fintech companies should not treat Aadhaar as a universal identity-verification method that can be used in any manner. The manner in which Aadhaar authentication, electronic KYC or offline Aadhaar verification may be used depends on the applicable Aadhaar framework and the legal status of the entity carrying out the verification. Fintech companies should therefore first establish whether they or their regulated partner are permitted to use the proposed Aadhaar-based mechanism.
Customers should also understand why Aadhaar-related information is being requested and how it will be used. Aadhaar information should not be unnecessarily displayed, copied, transferred or retained merely because it was obtained during onboarding. The technical design of the onboarding journey should therefore support masking, access controls, secure transmission and restricted storage wherever applicable.
Video KYC and Remote Customer Verification
Video-based Customer Identification Process, commonly referred to as V-CIP or Video KYC, has become particularly important for digital-first financial services. RBI's regulatory framework permits V-CIP for specified KYC purposes, subject to prescribed controls, and RBI continues to refer regulated entities to the V-CIP requirements contained in its KYC Master Direction. Video KYC should not be treated as an ordinary video conversation between an employee and a customer. Its purpose is to establish that the individual being verified is genuinely present and that the identity information being provided relates to that person.
The technology supporting Video KYC should therefore be capable of maintaining the integrity of the process. Appropriate safeguards may include live interaction, liveness testing, secure recording, restricted access, document verification and fraud-detection controls. This area has become even more important with the growth of AI-generated images, voice cloning and deepfake technology. A weak remote-verification system can potentially be manipulated using synthetic identities or altered videos. Fintech companies providing V-CIP infrastructure should therefore regularly review whether their fraud controls remain effective against newer forms of identity manipulation.
KYC for Companies, LLPs, Partnerships and Other Legal Entities
Business KYC is generally more complicated than individual customer onboarding because the fintech or regulated entity may need to understand both the organisation and the individuals who ultimately own or control it. If the customer is a company, LLP, partnership, trust or other legal entity, verification may involve incorporation or registration documents, PAN, registered-office information, details of authorised persons and beneficial ownership information.
Beneficial-owner identification is particularly important because financial crime can be concealed through complex corporate structures. An organisation may be owned through several holding companies, partnerships, trusts or overseas entities, making it difficult to identify the natural individuals who ultimately exercise ownership or control. A properly designed business-onboarding system should therefore allow the organisation to record ownership chains and identify the persons exercising ultimate control where required. Simply uploading a certificate of incorporation should not automatically be treated as completion of business KYC.
Central KYC Records Registry and CKYC
The Central KYC Records Registry, or CKYCR, was established to create a centralised repository of customer KYC records. Under the RBI KYC framework, regulated entities are required to capture prescribed customer KYC records and upload them to CKYCR within the applicable period. RBI's current regulatory material states that KYC records are to be uploaded to CKYCR within 10 days from commencement of an account-based relationship. It also provides for communication of the KYC Identifier and updating of changed customer information.
For fintech companies supporting banks or NBFCs, CKYC responsibilities should be properly mapped. For example, the fintech may collect the documents through its application, another service provider may perform document validation, and the regulated lender may ultimately upload the record to CKYCR. Without clearly defined responsibilities, incomplete data or delayed updates may fall between different service providers. Therefore, contracts and operational procedures should specify who is responsible at every stage.
KYC Is Not Limited to Customer Onboarding
An important misconception is that KYC ends once the customer's account has been opened. In reality, KYC forms part of an ongoing customer-risk management process. Regulated entities are expected to monitor customer relationships and transactions to ensure that financial activity remains consistent with their understanding of the customer and the customer's risk profile. If a customer who normally carries out small domestic transactions suddenly begins processing unusually large or complex transactions, this may require further investigation.
Similarly, significant changes in ownership, business activity, address or customer behaviour can affect the risk profile originally assigned during onboarding. RBI's KYC framework also contains provisions concerning periodic updating of KYC information and intensified monitoring of higher-risk customers. Fintech platforms should therefore be designed to support continuing compliance rather than treating onboarding as a one-time verification exercise.
Why Data Privacy Is Especially Important for Fintechs
Fintech companies often hold information that reveals far more about an individual than ordinary contact details. Banking transactions can indicate where a person shops, how much the individual earns, whether the individual has outstanding loans, what recurring expenses are being paid and how financially stable the customer may be. Credit information may show repayment behaviour and borrowing history. Location information may reveal where the customer lives or works. Device information and behavioural information can reveal how customers interact with an application.
A data breach involving this information can expose customers to financial fraud, impersonation, account takeover, unauthorised loans and sophisticated phishing attacks. Data privacy should therefore not be treated merely as the publication of a privacy policy on the fintech's website. It requires organisations to understand exactly what data they collect, why they collect it, where it is stored, who can access it, whom it is shared with and when it will be deleted.
India's Digital Personal Data Protection
India's privacy framework has undergone an important transition with the enactment of the Digital Personal Data Protection Act, 2023 and notification of the Digital Personal Data Protection Rules, 2025. However, fintech companies need to understand the phased commencement of this. The Central Government issued the commencement notification on November 13, 2025. Certain provisions concerning the Data Protection Board and institutional matters became operational immediately. Another group becomes effective one year after notification, while many of the substantive provisions covering processing, notice, consent, Data Fiduciary obligations, rights and related matters become effective 18 months after November 13, 2025, i.e. from May 13, 2027.
The DPDP Rules follow a similar phased approach. Rules dealing with areas including notice, security safeguards, breach intimation and several operational obligations are scheduled to commence after the 18-month transition period. Therefore, as of September 2026, fintech companies should be careful not to describe every substantive DPDP obligation as already enforceable. At the same time, organisations should not wait until May 2027 before preparing. Consent architecture, privacy notices, data inventories, customer-rights mechanisms, vendor contracts and deletion systems may require substantial technology development.
What Consent Means in a Fintech Environment
Consent is one of the most important issues for digital financial services because customers are frequently asked to approve multiple activities during onboarding. A borrower may be asked to consent to accessing financial information, checking credit history, verifying identity, communicating with third parties and receiving promotional communication. These activities should not automatically be bundled together.
Under the DPDP, where consent is relied upon for processing, the Act provides for consent that is free, specific, informed, unconditional and unambiguous and indicated through clear affirmative action. The substantive consent provisions form part of the later commencement schedule discussed above. This approach means that consent should be connected to an understandable and identifiable purpose. A statement such as “By clicking continue, you agree to everything we may do with your information” provides very little meaningful transparency. Fintech platforms should instead explain why particular data is required and what processing it enables.
Consent Should Be Granular Rather Than Bundled
Granular consent means separating permissions according to their purpose. Consider a customer applying for a personal loan. The lender may require identity information for KYC, financial information for underwriting and certain device permissions for completing remote verification. The lender may also want to send promotional messages about future products.
These purposes are not identical. The customer should not necessarily have to accept unrelated advertising simply to complete a loan application. Similarly, consent to retrieve financial information for underwriting should not automatically become unrestricted permission to use the customer's transaction history for unrelated profiling. Granular consent gives customers a clearer understanding of their choices and creates a better audit trail for the fintech.
Digital Lending and Explicit Customer Consent
Consent requirements are especially important in digital lending. RBI's regulatory framework emphasises need-based collection of borrower information, clear audit trails and prior explicit consent. It also requires borrowers to be given discretion concerning the use of specific data. RBI material further states that digital lending applications should not indiscriminately access mobile resources such as contact lists, call logs and files; limited one-time access to facilities such as camera, microphone or location may be taken where necessary for onboarding or KYC with explicit consent.
This means a digital lending application should not request broad mobile permissions simply because the operating system technically allows it. Every permission should have a genuine and identifiable purpose. A lending application requesting access to the customer's complete contacts list, photo library and call history without a clear regulatory or functional justification creates serious privacy concerns.
Data Minimisation Should Be Built Into Product Design
Data minimisation means collecting only the information genuinely necessary for the identified purpose. This is particularly important for fintech companies because digital technology makes it easy to collect information at scale. Product teams may sometimes request additional data on the assumption that it “might be useful later”. This creates unnecessary privacy and cybersecurity risk.
Before adding a new information field or mobile permission, a fintech should ask why the information is needed, what decision it supports, how long it will be required and whether the same objective can be achieved using less intrusive information. Reducing unnecessary collection also reduces the impact of a future security incident. Information that was never collected cannot be stolen from the organisation's systems.
Privacy Notices Should Be Clear and Meaningful
Privacy notices should help customers understand what happens to their information rather than merely protect the company through lengthy legal wording. The DPDP Rules provide that the notice given to a Data Principal must be understandable independently and give a clear account of relevant personal data and the specified purposes of processing. These operational notice requirements are scheduled to come into force according to the notified commencement timetable. For fintech companies, an effective privacy notice should accurately reflect the actual technical environment.
If customer information is being sent to a credit bureau, KYC service provider, cloud provider, regulated lender, analytics provider or collection agency, the organisation's data-governance documentation should account for those relationships. Fintech companies should avoid copying another company's privacy policy. A policy may appear legally sophisticated but still be inaccurate if it does not reflect the organisation's actual data-processing activities.
Sharing Customer Data with Banks, NBFCs and Service Providers
Fintech businesses generally operate through a large network of service providers. A single digital loan may involve a regulated lender, Lending Service Provider, KYC provider, credit-information company, payment gateway, cloud provider, communication service, analytics provider and recovery agency. Every additional organisation increases the number of locations where customer information can potentially be accessed.
Therefore, third-party sharing should be governed through clearly defined contractual and technical controls. Contracts should specify the purpose of processing, permitted access, confidentiality obligations, security standards, breach reporting, subcontracting requirements, retention periods and deletion or return of information when the relationship ends. Access should also be limited on a need-to-know basis. A vendor providing SMS services, for example, should not automatically receive unrestricted access to a customer's complete financial profile.
Data Storage and Localisation
Data localisation is another area where fintech companies need to distinguish general privacy law from financial-sector requirements. A fintech cannot simply assume that every category of customer information is governed by one universal localisation rule. Specific RBI-regulated activities may carry additional requirements. In digital lending, RBI's framework has prescribed requirements concerning borrower data, including storage arrangements and restrictions on information that may be stored by Lending Service Providers and Digital Lending Applications. RBI's regulatory handbook states that digital-lending data is to be stored on servers located in India.
Therefore, fintech companies should analyse the particular financial service being provided before selecting cloud regions, backup locations and disaster-recovery systems. The organisation should know not only where its primary database is hosted but also where backups, logs and vendor copies are located.
Data Retention and Deletion
Data retention creates an important tension between privacy principles and financial regulation. From a privacy perspective, information should generally not be retained indefinitely without a continuing purpose. However, financial institutions may be legally required to maintain transaction, KYC and other regulatory records for prescribed periods.
This means that a customer's request for deletion does not automatically require a regulated financial institution to erase every piece of information immediately. Fintech companies should therefore build a structured retention. Each data category should have an identified purpose, regulatory requirement and retention period. Once there is no continuing legal, regulatory or legitimate operational requirement for the information, the organisation should have a process for deleting or appropriately anonymising it. The important point is that records should not be retained merely because storage is inexpensive.
Maintaining Consent Records and Audit Trails
A fintech should be capable not only of obtaining consent but also of proving what the customer actually agreed to. This becomes important when a customer later challenges the use of information or when a regulator examines the organisation's consent practices. The system should therefore maintain an appropriate record of when consent was obtained, what purpose was communicated, what version of the notice was displayed and what action the customer took.
If the organisation subsequently changes the purpose of processing, it should determine whether a new notice or fresh consent is required. Consent withdrawal should also be reflected throughout relevant systems rather than only in the application's user interface. For example, if the customer opts out of marketing, the request should reach the CRM system, communication tools and relevant marketing vendors rather than simply changing a setting displayed in the mobile app.
Cybersecurity Is an Essential Part of Data Privacy
A privacy policy is meaningless if customer information is not properly protected. Fintech companies are particularly attractive targets for cybercriminals because financial and identity information can be monetised quickly. Security measures should therefore extend throughout the information lifecycle. Sensitive information should be protected during collection, transmission, storage and deletion. Access should be restricted according to employee responsibilities. Administrative accounts should be monitored carefully, and employees should not have unlimited access to customer information simply because they work within the organisation.
Fintech companies should also pay close attention to API security because modern financial services often exchange data through APIs connecting multiple organisations. A weakness in a third-party integration may expose information even if the fintech's core database is otherwise secure.
Managing Personal Data Breaches
No fintech should assume that a cyber incident can never happen. Even organisations with sophisticated cybersecurity systems can experience phishing attacks, credential theft, ransomware, software vulnerabilities or vendor breaches. For this reason, incident-response procedures should exist before an incident occurs. The fintech should know who will investigate a suspected breach, who will make regulatory decisions, who will contact affected service providers and who will approve customer or regulator communications.
The DPDP Rules contain specific requirements relating to reasonable security safeguards and personal-data breach intimation, which are scheduled to become operational under the notified commencement timeline. Vendor contracts should also contain clear incident-notification provisions. A fintech cannot manage its reporting responsibilities effectively if an outsourced service provider waits several days before informing it that customer information has been compromised.
Marketing Consent Should Be Kept Separate
Financial data can be extremely valuable for marketing purposes. Transaction patterns may indicate whether a customer is likely to need a loan, insurance policy, investment product or credit card. However, the fact that a fintech possesses such information does not automatically mean that every possible marketing use is appropriate.
A customer may have provided information solely to complete KYC or obtain a particular financial service. Using the same data for unrelated profiling or promotional communication should be assessed separately. Fintech companies should therefore distinguish operational or legally required processing from optional marketing activities. This separation also makes consent management easier because a customer can withdraw promotional permissions without interfering with information that must continue to be processed for regulatory purposes.
Artificial Intelligence, Credit Scoring and Customer Data
Artificial intelligence and automated decision-making are becoming increasingly important in fintech. Algorithms can help lenders assess credit risk, identify fraud, detect unusual transactions and personalise products. These capabilities can improve efficiency, but they also create new data-governance questions.
An algorithm may technically be capable of analysing hundreds of variables, but this does not mean the fintech should automatically collect every available piece of information. The organisation should understand where the information came from, why it is being used and whether it is appropriate for the relevant financial decision. Fintech companies should also ensure that important models are tested and monitored because inaccurate data can produce inaccurate outcomes at scale.
If an automated credit-assessment system relies on outdated, incomplete or incorrectly linked customer information, thousands of customers could potentially be affected before the error is identified. Human oversight, model governance and proper data-quality controls therefore remain important even where decision-making becomes highly automated.
Children's Personal Data and Fintech Products
Fintech companies may sometimes process information relating to children, particularly through family finance applications, prepaid products, education-related financial services or investment platforms. The DPDP Act establishes additional requirements concerning children's personal data, including provisions relating to verifiable parental consent and restrictions on specified forms of tracking, behavioural monitoring and targeted advertising, subject to the statutory framework and notified exemptions. The substantive provisions relating to these obligations form part of the phased commencement schedule.
Fintech companies whose products may be used by minors should therefore consider age verification and parental-consent architecture during product development rather than attempting to address the issue later through generic terms and conditions.
Withdrawal of Consent Does Not Cancel Legal Obligations
Fintech companies should also understand that not every processing activity depends on consent. Financial institutions may be legally required to collect, monitor, report or retain certain information. For example, an institution may need to maintain KYC records, transaction information or fraud-investigation records even after the customer no longer wishes to receive marketing communication.
Therefore, withdrawal of consent for one purpose should not automatically be interpreted as a requirement to erase every record connected with the customer. The correct approach is to identify the legal basis and purpose associated with each processing activity. Optional marketing may stop after consent is withdrawn, while information required for compliance with financial laws may continue to be retained for the prescribed period.
Vendor Management Is a Major Fintech Privacy Risk
Fintech companies frequently focus their security efforts on internal systems while overlooking third-party service providers. In practice, customer data may pass through numerous external systems. An organisation may use one provider for Video KYC, another for cloud hosting, another for SMS communication, another for customer support and another for analytics.
Each vendor therefore creates additional data exposure. Vendor due diligence should consider the type of information being processed, technical security standards, access controls, incident history, subcontractors, storage locations and deletion practices. Contracts should also ensure that information cannot continue to be retained indefinitely by a vendor after the service relationship has ended. Vendor risk should be reviewed periodically rather than only at the beginning of the contract.
Internal Access to Customer Data Should Be Controlled
Privacy compliance does not relate only to external sharing. Unauthorised access by employees can also create serious risk. Fintech companies should apply role-based access controls so that employees can access only the information necessary for their responsibilities.
A customer-service employee may need to view certain account information but may not require access to complete KYC documents or financial statements. Similarly, a marketing employee should not automatically have access to raw banking information simply because the organisation possesses it. Access logs should be maintained so that unusual internal access can be detected and investigated.
Privacy by Design Should Become Part of Product Development
The most effective approach to fintech privacy is to address compliance before a product or feature is launched. If legal and compliance teams become involved only after a new technology has already been developed, privacy problems can be difficult and expensive to correct.
For example, a new feature may already have been designed to collect unnecessary device permissions, or customer information may already be flowing to multiple external vendors. A privacy-by-design approach requires product, technology, security and compliance teams to assess data requirements during the design stage. Every new API integration, AI feature, customer permission, analytics tool and third-party service should therefore undergo an appropriate privacy and regulatory review.
Preparing Fintech Businesses for Full DPDP Implementation
The phased implementation of the DPDP framework gives fintech companies an important preparation period. Businesses should use this period to identify where personal information exists across their organisation. A fintech may discover that customer information is spread across mobile applications, loan-management systems, CRMs, cloud storage, email accounts, spreadsheets, call-centre tools, backups and vendor systems.
Unless this information is properly mapped, the organisation may find it difficult to respond to consent withdrawals, deletion requirements, customer requests or security incidents. Companies should therefore develop an accurate data inventory, review consent journeys, update notices, examine vendor contracts and establish technical processes for retention and deletion. Waiting until the final commencement date may leave insufficient time to correct historical data practices.
Common KYC and Privacy Mistakes Made by Fintechs
Some of the most serious compliance problems arise when the organisation's published policies and its actual technology do not match. A fintech may state that it collects only necessary information while its mobile application requests broad permissions. It may state that customers can withdraw consent even though the backend system has no mechanism to stop processing. It may promise deletion while multiple vendor copies and backups remain indefinitely.
Other recurring risks include treating KYC as a one-time exercise, requesting unnecessary customer information, failing to properly identify beneficial owners, using one checkbox for several unrelated processing activities, giving vendors excessive database access and launching new data uses without compliance review. The solution is not simply to create longer policies. Organisations need to test whether their actual operational processes follow the policies they have written.
Building an Effective KYC, Privacy and Consent
An effective fintech compliance should connect customer identification, AML controls, privacy management, cybersecurity and vendor governance. The organisation should first understand every category of information collected from customers and identify its purpose. It should then determine whether the information is required because of KYC or another financial regulation, required for providing the product, or collected for an optional commercial purpose.
The fintech should identify where the information is stored, which employees can access it, which vendors receive it and how long it is retained. Consent mechanisms should then be matched to these actual data flows. KYC processes should be monitored for quality, while periodic updating and transaction-monitoring systems should support continuing due diligence. Vendor relationships should be reviewed regularly, and cybersecurity controls should be tested rather than assumed to be effective. Most importantly, senior management should understand that customer-data protection is not solely the responsibility of the legal, compliance or information-security team. It is an organisation-wide governance responsibility.
Conclusion
KYC, data privacy and consent are now central to responsible fintech operations in India. KYC helps financial institutions verify customers and reduce risks such as fraud, money laundering and identity misuse, while data privacy focuses on how personal and financial information is collected, stored, shared and protected. Consent ensures that customers are properly informed and are given meaningful control over the use of their information wherever permission is required. Together, these obligations create a framework that supports both regulatory compliance and customer trust.
For fintech companies, effective compliance requires more than collecting documents or adding consent checkboxes to an application. Customer data should have a clear purpose, lawful basis, defined retention period, restricted access and appropriate security safeguards. As India’s DPDP framework continues to develop, fintech businesses should strengthen their internal systems, review vendor relationships and integrate privacy into product design. Strong KYC, transparent consent and responsible data governance can help fintechs manage regulatory risk and build long-term customer confidence.
Frequently Asked Questions
Q1. What is KYC in fintech?
Ans. KYC, or Know Your Customer, is the process used by financial institutions and fintech platforms to verify the identity of customers. It helps prevent fraud, money laundering, identity theft and misuse of financial services.
Q2. Why is data privacy important for fintech companies?
Ans. Fintech companies handle sensitive information such as PAN, bank details, transaction history, income records and credit information. Proper data privacy practices help ensure that this information is collected, stored, used and shared securely and only for legitimate purposes.
Q3. Is customer consent mandatory for fintech companies?
Ans. Consent may be required when customer data is processed on the basis of permission. However, some processing may also be required by law or regulation. Fintechs should clearly distinguish between mandatory regulatory processing and optional consent-based activities.
Q4. Can a fintech collect any customer data it wants?
Ans. No. Fintech companies should collect only information that is necessary for a specific and legitimate purpose. Excessive collection of personal information or unnecessary device permissions can create privacy and regulatory risks.
Q5. Can fintech apps access a customer's contacts and call logs?
Ans. Digital lending applications should not indiscriminately access mobile phone resources such as contact lists, call logs and files. Access to device features should be limited to what is genuinely required and should follow applicable RBI requirements.
Q6. What is granular consent?
Ans. Granular consent means obtaining separate permission for different purposes. For example, consent for KYC verification should be distinguished from consent for marketing, promotional communication or unrelated data sharing.
Q7. Can customers withdraw their consent?
Ans. Where processing depends on consent, customers should generally be able to withdraw that consent through an appropriate mechanism. However, withdrawal does not necessarily require deletion of information that must be retained for legal, KYC, AML or regulatory purposes.
Q8. What is CKYC?
Ans. CKYC refers to the Central KYC Records Registry system, which maintains centralised KYC records of customers. Regulated entities may be required to upload and update KYC information in accordance with applicable regulatory requirements.
Q9. Is Video KYC allowed in India?
Ans. Yes, Video-based Customer Identification Process, or V-CIP, is permitted for specified purposes under RBI's KYC framework, subject to prescribed safeguards relating to live verification, consent, identity checks and security.
Q10. How long should fintech companies retain KYC data?
Ans. The retention period depends on the applicable law and regulatory requirements. Certain KYC and transaction records may need to be retained for prescribed periods even after the customer relationship has ended.
- 16 Sep, 2026
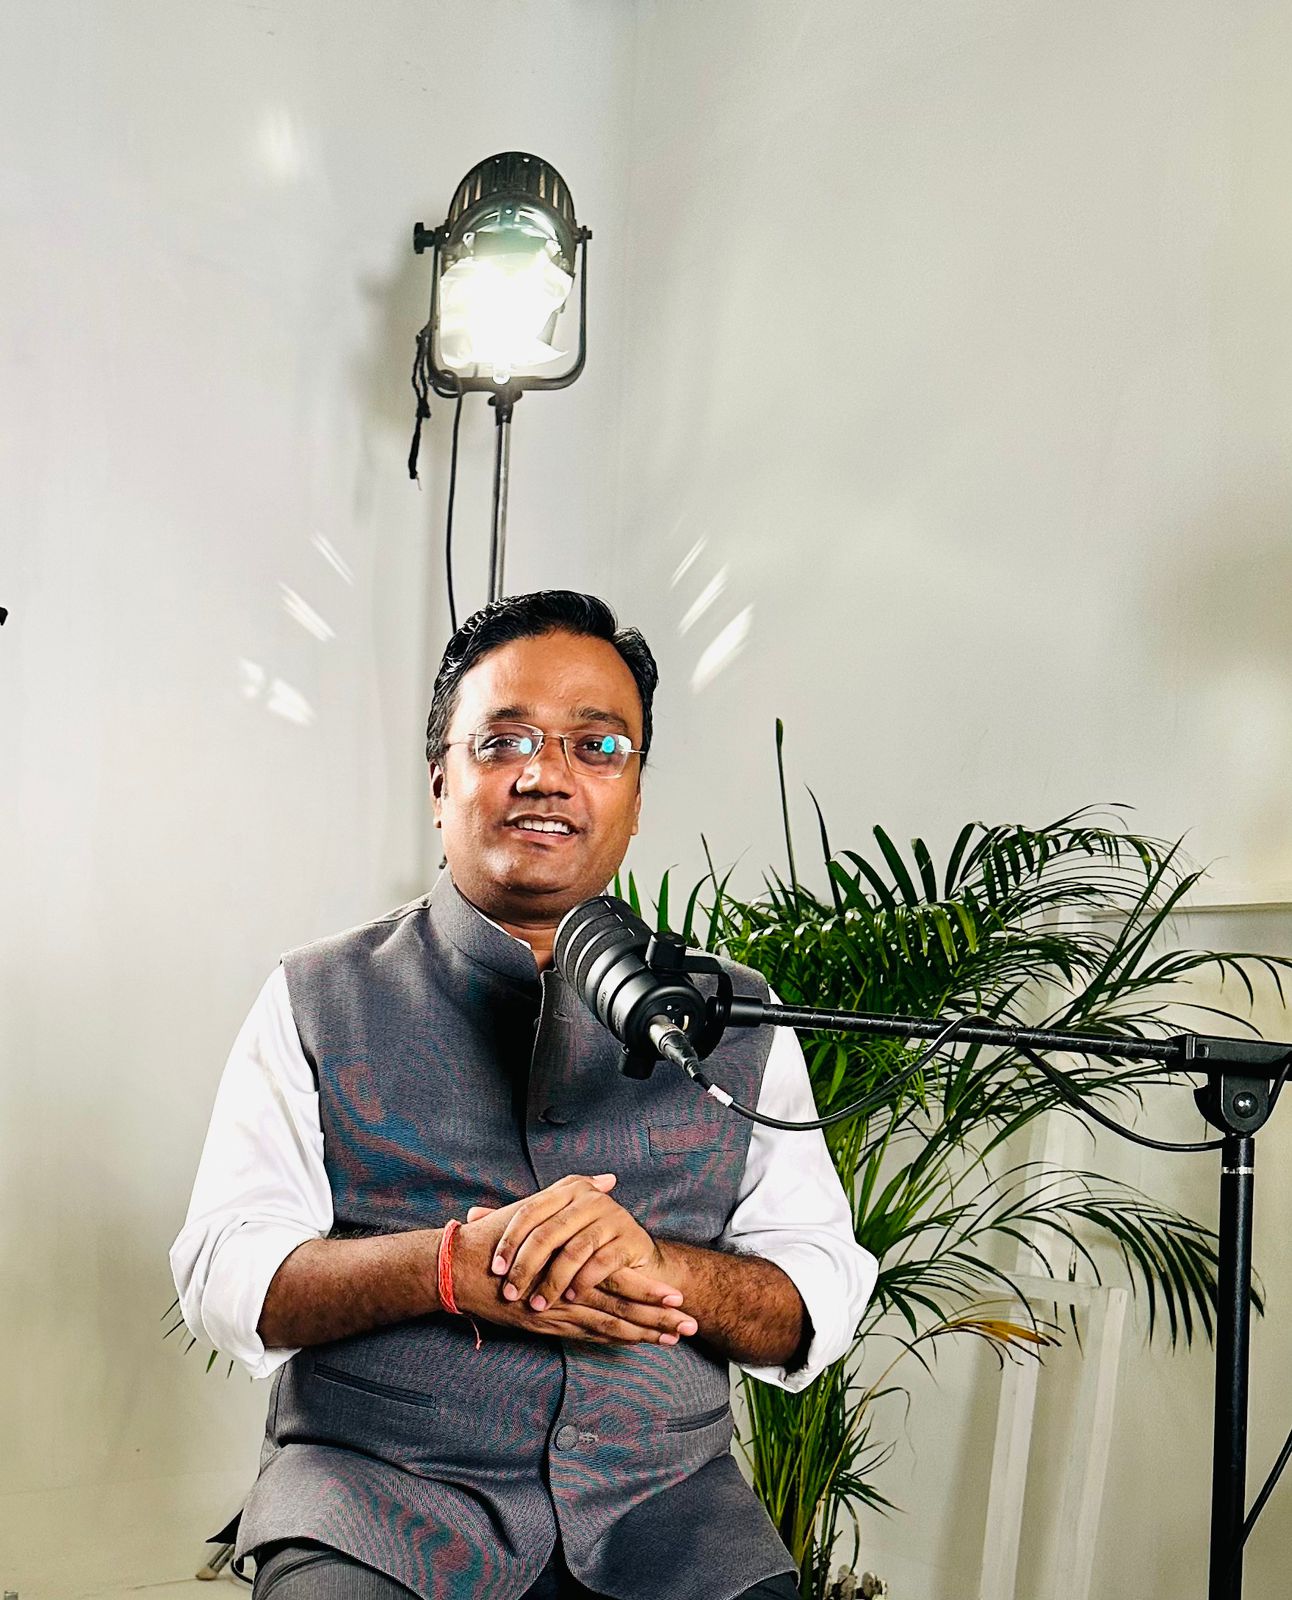 CA Manish Mishra
- Starting Up
CA Manish Mishra is the Co-Founder & CEO at GenZCFO. He is the most sought professional for providing virtual CFO services to startups and established businesses across diverse sectors, such as retail, manufacturing, food, and financial services with over 20 years of experience including strategic financial planning, regulatory compliance, fundraising and M&A.