Search GrowthX Learning Content
Post-Licence Compliance for Insurance Intermediaries
Obtaining registration from the Insurance Regulatory and Development Authority of India (IRDAI) allows an insurance intermediary to undertake specified activities. However, registration is only the beginning of its regulatory responsibilities. The intermediary must continue to satisfy the conditions applicable to its business, supervise its operations and protect policyholders’ interests.
Post-licence compliance includes maintaining financial eligibility, employing qualified personnel, following fair sales practices, submitting regulatory returns, safeguarding customer information and handling complaints. These responsibilities continue throughout the intermediary’s operations and should form part of its daily business processes.
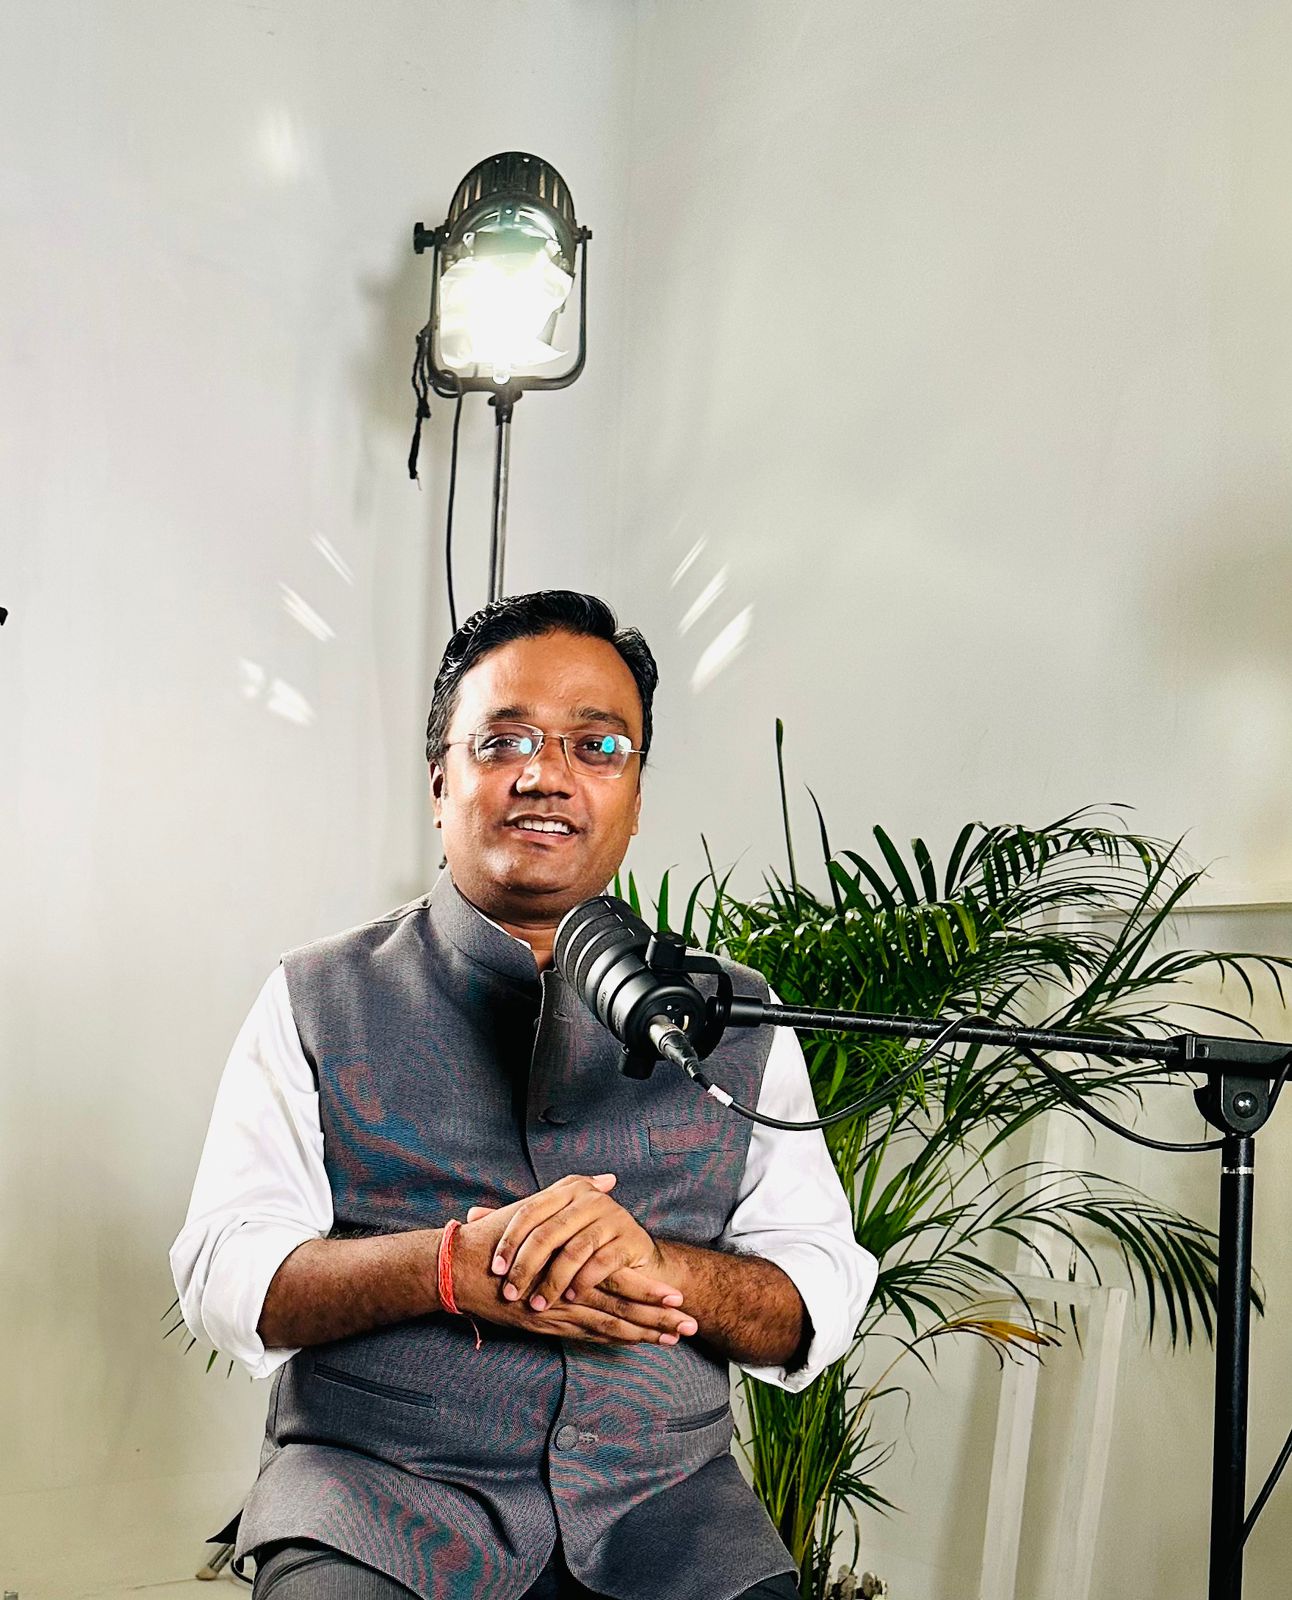
In this article, CA Manish Mishra talks about Post-Licence Compliance for Insurance Intermediaries.
Understanding the Applicable Compliance Requirements
Insurance intermediaries include insurance brokers, corporate agents, insurance web aggregators, insurance marketing firms, third-party administrators, surveyors and loss assessors, and insurance repositories. Each category performs different functions and is subject to its own regulatory.
An intermediary must identify the requirements applicable to its registration category, business activities and certificate conditions. It should also track amendments, circulars and regulatory directions affecting those requirements. A broker’s financial obligations, for example, should not automatically be applied to a corporate agent, while a web aggregator needs controls suited to digital comparisons and lead management. A practical compliance should explain what must be done, who is responsible, when the obligation arises and what evidence must be retained. This helps prevent important requirements from being overlooked between departments.
Maintaining Registration and Paying Applicable Fees
An insurance intermediary must maintain its registration in accordance with the prevailing. This includes paying applicable regulatory fees, completing prescribed procedures and complying with the conditions attached to its certificate.
Management should monitor changes affecting registration continuity and update its compliance calendar accordingly. Where transition arrangements or fresh certificate procedures apply, the intermediary should identify the relevant documents and complete the process within the prescribed period. The registration file should contain the current certificate, applications, payment acknowledgements and regulatory correspondence. Assigning responsibility for these records helps the business demonstrate its registration status and respond promptly to regulatory enquiries.
Remaining Within the Authorised Scope of Business
An intermediary should undertake activities permitted under its registration category. Before introducing a new service, distribution arrangement or commercial partnership, it should assess whether the proposal falls within its authorised scope. For example, a business registered for a particular distribution function should review whether a proposed advisory, technology or claims-related service is permitted and whether additional conditions apply.
The assessment should consider the actual nature of the work, rather than relying only on the description used in an agreement. A review before signing contracts can identify approval requirements, conflicts of interest, staffing needs and restrictions on outsourcing. This allows the business to resolve compliance issues while the arrangement is still being planned.
Maintaining Capital, Net Worth and Deposits
Financial eligibility must be monitored throughout the intermediary’s operations. The applicable capital, net-worth and deposit requirements depend on its category and regulatory. An intermediary may satisfy financial requirements at registration but experience a decline in net worth because of operating losses or other transactions. Management should therefore assess the effect of dividends, exceptional expenditure, related-party dealings and proposed changes in capital before approving them.
Regular financial monitoring can identify an approaching shortfall early. A reasonable buffer above the prescribed minimum can also help absorb unexpected costs. Where certificates or financial statements must be submitted to the regulator, the underlying calculations should be checked and supported by reliable records.
Maintaining Professional Indemnity Insurance
Professional indemnity insurance provides protection against specified liabilities arising from professional services. Where this cover is required, the intermediary must maintain a policy that meets the applicable regulatory conditions. The review should cover the insured activities, policy limit, exclusions, excess and notification requirements.
A policy may remain active but become inadequate if the intermediary expands its services or handles substantially more business. Renewals should be arranged without a coverage gap. Employees responsible for complaints and legal matters should also understand when a circumstance may need to be reported to the insurer. Timely notification can be important to the availability of protection under the policy.
Establishing Effective Governance
Effective governance requires clear responsibility for compliance and sufficient authority for responsible officers to carry out their duties. The principal officer and other designated personnel should have access to information and a direct reporting route to senior management. Compliance should influence business decisions from the planning stage. For example, launching a new digital sales channel may involve customer disclosures, payment arrangements, data protection and record retention.
These matters require coordination between sales, finance, technology and compliance teams. Management should receive periodic reports on pending filings, complaints, financial eligibility, personnel authorisations and corrective actions. These reports should identify the decisions or resources needed to resolve outstanding issues.
Employing Qualified and Authorised Personnel
Employees involved in insurance solicitation and other regulated activities should satisfy the qualifications, training, examination and authorisation requirements applicable to their roles. An intermediary should maintain records showing each employee’s eligibility, training history, authorisation and assigned responsibilities. These records should be reviewed when an employee joins, changes roles, transfers branches or leaves the organisation.
Access to sales systems and customer information should reflect current responsibilities. When an employee leaves, access should be removed promptly and pending customer matters reassigned. Changes involving the principal officer or other essential personnel should also be assessed for regulatory reporting and appointment requirements.
Following Fair Sales Practices
Fair sales practices help customers understand the insurance they are purchasing. The intermediary should explain relevant benefits, premium commitments, exclusions, waiting periods, deductibles and other conditions that could affect the customer’s decision.
For example, a customer may choose a health insurance policy because of its lower premium without understanding the impact of a co-payment. A clear explanation before purchase helps the customer assess the likely financial responsibility during a claim. Appropriate records should show what information was provided and why a recommendation was made. Sample file reviews, customer callbacks and analysis of cancellations can help management identify weaknesses in sales practices.
Managing Conflicts of Interest
Conflicts of interest can arise where an intermediary’s commercial incentives influence its recommendations or customer service. Relationships with insurers, group entities, vendors or referral partners may create situations requiring assessment and control. An intermediary should identify circumstances in which its interests could affect the customer’s treatment.
Internal procedures should explain how such circumstances will be disclosed, managed or avoided. Sales incentives deserve particular attention. Management should examine whether targets or rewards encourage employees to recommend unsuitable products, overlook customer needs or focus excessively on a particular insurer. Supervisory reviews should consider the reasons behind recommendations and the resulting customer outcomes.
Supervising Digital Sales and Communications
Digital insurance distribution requires oversight of the entire customer journey. Website content, advertisements, comparison tools, telephone scripts and electronic messages should provide accurate and understandable information. The intermediary should review how customers give consent, how their details are collected and how leads are shared.
Changes to product information should follow a controlled approval process so that outdated premiums or benefits do not remain visible. Testing should examine the sequence from advertisement to proposal submission. Important restrictions should appear at a stage when customers can meaningfully consider them. A qualification shown only after the customer has made a decision may fail to prevent misunderstanding.
Protecting Customer Information
Insurance intermediaries may handle identity records, financial details, medical information and claims documents. Unauthorised access or disclosure can cause serious inconvenience and harm to customers. Access should be limited according to job responsibilities. Customer information should be stored and transferred through approved systems, with appropriate safeguards against loss, misuse and accidental disclosure.
Vendor access also requires supervision. Where a service provider handles customer information, the intermediary should understand what data is shared, why access is necessary and how that access is controlled. Employees should receive practical guidance on secure document handling and the risks of using personal email accounts or uncontrolled messaging groups.
Strengthening Cybersecurity and Business Continuity
Cybersecurity supports the confidentiality, integrity and availability of the intermediary’s systems and information. Controls should be assessed against applicable regulatory requirements and the risks arising from the business’s operations. Practical measures include secure access, timely software updates, backups, monitoring and periodic security assessments. An incident-response process should identify who will investigate an event, preserve evidence, assess reporting requirements and coordinate recovery.
Business continuity planning should address how essential services will operate during a system outage, cyber incident or other disruption. Recovery arrangements should be tested so that management understands whether customer records, communications and servicing functions can be restored when needed.
Supporting KYC and Anti-Money Laundering Processes
An intermediary’s role in customer identification and anti-money laundering processes depends on its category, activities and insurer arrangements. Responsibilities should be documented clearly so that customer verification tasks are completed consistently. The process should identify who collects documents, who checks information and how incomplete or inconsistent records are escalated.
Employees should understand how to respond to unusual payment instructions or attempts to bypass established procedures. The intermediary should distinguish its own obligations from those of the insurer. It should assess any direct reporting requirement under the law applicable to the entity and avoid assuming that another party’s involvement removes its responsibilities.
Controlling Premium and Commission Transactions
Financial controls should allow transactions to be traced between customer records, insurer statements and the intermediary’s accounts. The business should document its authorised role in premium handling, remittances, refunds and commission receipt. Regular reconciliation can identify unmatched receipts, incorrect deductions and unexplained differences.
Exceptions should be investigated promptly because delays may affect customers and create errors in financial or regulatory reporting. Agreements and invoices should describe services accurately. The substance of a payment should be reviewed to determine whether it is permissible. Changing its description to a marketing, technology or support fee does not resolve an underlying compliance issue.
Handling Customer Complaints
A complaint-handling process should provide customers with an accessible route to raise concerns and receive a reasoned response. Complaints should be recorded, assigned to a responsible officer and tracked against applicable timelines. The record should include the issue, relevant policy details, communications, insurer coordination and the basis for closure.
Customers should receive clear information about available escalation routes where appropriate. Management should examine recurring complaints to identify broader problems. Repeated concerns about exclusions may indicate inadequate product explanations, while frequent servicing delays may reveal staffing or coordination weaknesses. Addressing the cause helps improve service beyond the individual complaint.
Providing Continuing Policyholder Service
The intermediary’s customer relationship often continues after the policy is issued. Depending on its authorised role, servicing may include assistance with renewals, endorsements, corrections, cancellations and claims documentation. Responsibilities should be assigned clearly so that customer requests do not remain pending between the intermediary and insurer.
Communications should explain the status of the request and any documents or action required from the customer. Claims assistance should be accurate and realistic. Employees should explain the process without making promises about settlement that are outside the intermediary’s authority.
Filing Accurate Regulatory Returns
Regulatory filings should be prepared from complete records that reconcile with the intermediary’s accounts and operating systems. Each submission should have an identified preparer, reviewer and authorised signatory. A compliance calendar should capture the returns, certificates and statements applicable to the intermediary’s category.
Sufficient time should be allowed for internal checking and obtaining any required professional certification. The final filing, supporting calculations, approvals and submission acknowledgement should be retained. Where information differs between reports, the reason should be documented so that the business can explain the difference consistently.
Reporting Material Changes
Changes involving ownership, control, management, the principal officer, business name, address or organisational structure should be assessed for regulatory approval and intimation requirements. The assessment should occur when the change is proposed.
Where prior approval is required, implementing the change first may create a breach that cannot be corrected through a routine later notification. Internal procedures should require relevant departments to involve compliance before completing material changes. This helps identify the necessary documents, approvals and timelines before contractual commitments are made.
Maintaining Records and Preparing for Inspections
An intermediary should maintain organised records that demonstrate how it has fulfilled its obligations. Relevant documents may include registration records, filings, agreements, policies, training records, customer communications and complaint files. Retention requirements should be assessed by record type because different documents may be subject to different periods and conditions.
Records should also be protected from unauthorised alteration and remain retrievable when needed. Inspection readiness depends on everyday recordkeeping. Documents should reflect actual practices, and employees should understand the processes described in internal policies. A policy that exists only on paper provides limited evidence of effective compliance.
Correcting Compliance Deficiencies
When a deficiency is identified, the intermediary should record the issue, its cause, the affected activities and the action required. Responsibility and a completion deadline should be assigned. Corrective action should address the underlying problem. An isolated mistake may require individual guidance, while repeated errors may indicate weaknesses in training, software or supervision.
Closure should include evidence that the change has been implemented and is operating effectively. Management should monitor overdue actions and assess whether similar problems exist elsewhere in the business.
Conclusion
Post-licence compliance is a continuing responsibility that connects registration conditions with everyday business conduct. It requires financial discipline, qualified personnel, fair sales practices, reliable records and effective customer service.
An intermediary that assigns clear responsibilities and reviews its controls regularly can identify problems earlier and respond more effectively to regulatory and operational changes. This approach supports business continuity and strengthens policyholder confidence.
Frequently Asked Questions (FAQ’s)
Q1. What is post-licence compliance for insurance intermediaries?
Ans. Post-licence compliance refers to the ongoing responsibilities an insurance intermediary must fulfil after obtaining registration from IRDAI. These include maintaining financial eligibility, employing qualified personnel, following fair business practices, submitting applicable returns and protecting customer information.
Q2. Are compliance requirements the same for every insurance intermediary?
Ans. No. Requirements differ according to the intermediary’s registration category and activities. Insurance brokers, corporate agents, web aggregators, insurance marketing firms and other intermediaries must follow their respective regulatory and registration conditions.
Q3. Must an intermediary maintain minimum net worth after registration?
Ans. Yes, where its applicable regulations prescribe a continuing net-worth requirement. The intermediary should monitor its financial position regularly because losses and other transactions can reduce net worth below the required level.
Q4. Is professional indemnity insurance compulsory for every intermediary?
Ans. Professional indemnity insurance is compulsory where the applicable regulations require it. The requirement, coverage limits and policy conditions depend on the intermediary’s category and circumstances. Businesses subject to this obligation should maintain adequate cover without interruption.
Q5. What responsibilities does the principal officer have?
Ans. The principal officer oversees the intermediary’s regulated activities within the applicable. Responsibilities generally include supervising business conduct, supporting regulatory compliance, overseeing authorised personnel and coordinating responses to regulatory matters.
Q6. Can any employee sell insurance products?
Ans. Employees undertaking insurance solicitation must meet the qualification, training, examination and authorisation requirements applicable to their roles. Employment with a registered intermediary does not, by itself, authorise an individual to sell insurance.
Q7. What information should customers receive before purchasing insurance?
Ans. Customers should receive a clear explanation of relevant benefits, premiums, exclusions, waiting periods, deductibles and other important conditions. The explanation should help them understand whether the policy meets their needs and what limitations may apply.
Q8. How should an intermediary handle customer complaints?
Ans. The intermediary should record the complaint, assign responsibility, investigate the issue and respond within the applicable timeline. It should retain communications and closure records, coordinate with the insurer where necessary and explain available escalation routes.
Q9. What customer information must an intermediary protect?
Ans. An intermediary should safeguard the personal and confidential information it handles, including identity documents, contact details, financial information, medical records and claims documents. Access should be restricted to authorised persons with a legitimate business need.
Q10. What changes may require regulatory approval or intimation?
Ans. Changes involving ownership, control, management, the principal officer, business name, address or organisational structure may trigger approval or reporting requirements. The applicable process should be checked before implementing the proposed change.
- 28 Oct, 2026
 CA Manish Mishra
- Starting Up
CA Manish Mishra is the Co-Founder & CEO at GenZCFO. He is the most sought professional for providing virtual CFO services to startups and established businesses across diverse sectors, such as retail, manufacturing, food, and financial services with over 20 years of experience including strategic financial planning, regulatory compliance, fundraising and M&A.